


WardBee by ScanComb
Know what's actually verified.
WardBee checks your AWS accounts and GitHub or GitLab repositories against ISO 27001, SOC 2, NIST, CIS and the EU CRA. Every pass has an evidence trail. Everything unverified is shown as unknown, never as green.
Control status
ISO 27001 · 93 controls- PASSVerified by current evidence48
- FAILVerified as not meeting the control6
- UNKNOWNNo evidence found. Not assumed compliant12
- STALEEvidence aged past its freshness window5
- MANUALNeeds a reviewed policy or document22
AI explains
Plain-language explanations and fix suggestions for your own environment. AI never overrides an automated check result. AI-checked documents keep their own review label.
Your decisions.
Backed by evidence.
- Read-only access
- Timestamped evidence
- AI never overrides an automated check
We won't guess.
Only verified results count. Everything else is shown by name, never rounded toward green.
Counted
- Pass
- Fail
Never counted as a pass
- Unknown
- Stale
- Conflict
- Manual
- Error
Not applicable is tracked separately and excluded from the score.
Integrations
Connect your cloud and code. Get the full picture.
WardBee connects with read-only access, collects evidence on every sync and maps it to the frameworks you report on. Review access and security
- Policies & docs
- AWS
- GitHub
- GitLab
- AzurePreview
WardBeeby ScanComb
- Collect evidence automaticallyTimestamped on every sync.
- Read-only accessWardBee never changes your systems.
- Mapped to your frameworksISO 27001, SOC 2, NIST, CIS and the EU CRA.
How it works
Turn technical evidence into compliance.
- 01
Connect
Link cloud accounts and repositories with read-only access.
- 02
Collect
Gather evidence each time your systems sync.
- 03
Evaluate
Match evidence to each control. Only verified results count.
- 04
Report
Export an evidence package with human sign-off in the loop.
Frameworks
- ISO 2700148 / 93 passed6 fail · 39 not verified
- SOC 229 / 61 passed3 fail · 29 not verified
- NIST CSF59 / 106 passed4 fail · 43 not verified
- EU CRA13 / 35 passed3 fail · 19 not verified
Mapped to the
frameworks you report on.
WardBee
Every result has an evidence trail.
Automated checks give a clear pass or fail, with the evidence attached. Policies and documents go through manual evidence reviews, each labeled by who reviewed them: you, a colleague, AI, a ScanComb consultant or your auditor. AI explains results. It never changes an automated result.
See how WardBee works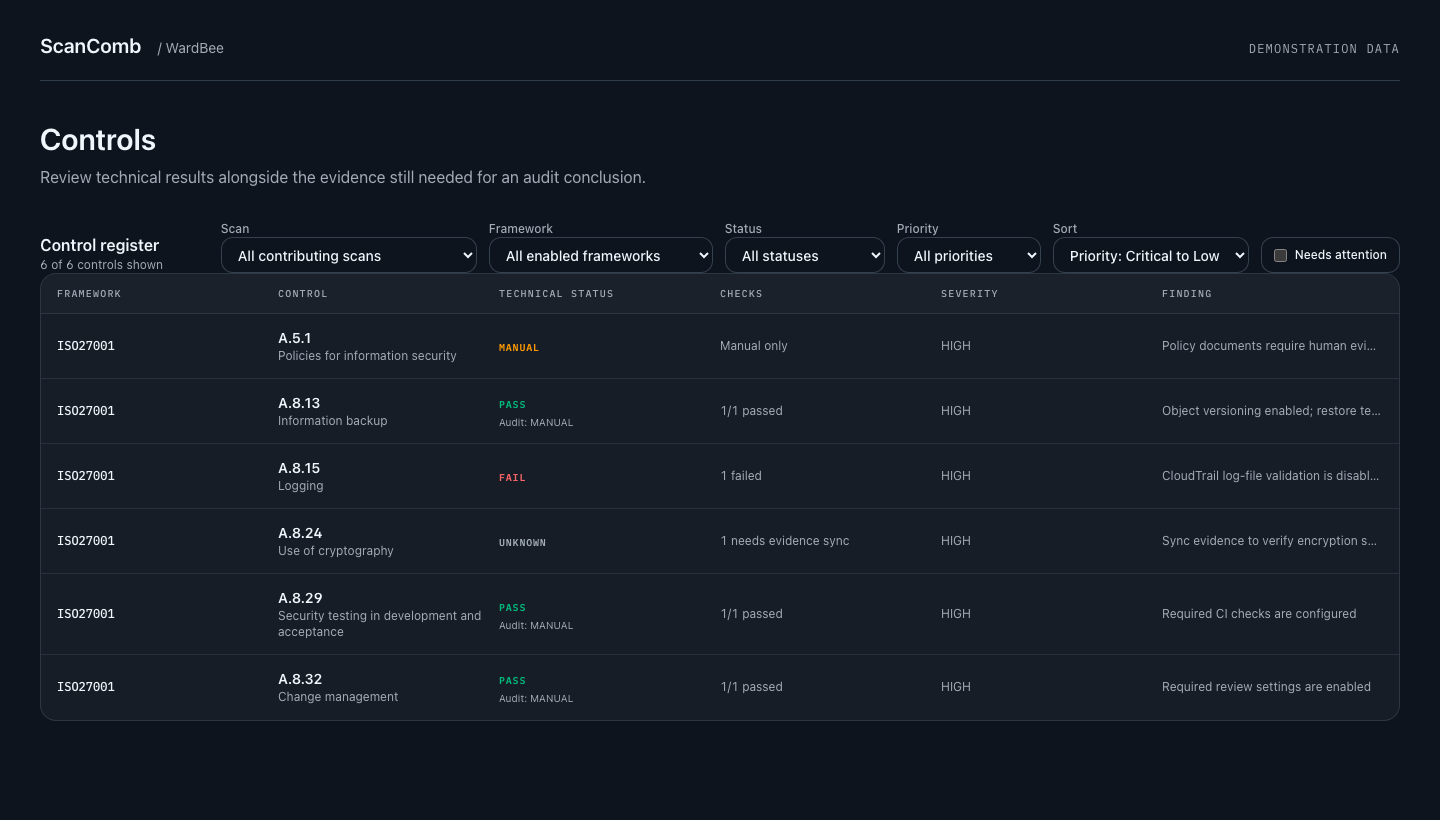 Demonstration data · Open full-size screenshot
EU regulation
CRA reporting duties already apply. NIS2 reaches your suppliers.
CRA reporting duties have applied since 11 September 2026, with full application from 11 December 2027. NIS2 customers now ask their suppliers for proof, public buyers ask how sovereign their SaaS vendors are, and automotive customers ask for TISAX.
Framework Watch W45 · 26 Oct – 10 Nov 2026
All issues →SOC 2 gets its first rewrite since 2017, and NIS2 moves from law to audits
- SOC 2High impactAICPA proposes the 2027 SOC 2 Trust Services Criteria
- PCI DSSMedium impactPCI SSC explains who counts as a service provider and what they owe customers
- EU CRAMedium impactFirst horizontal CRA standards, EN 40000-1-1 and -1-2, due on 17 November
AI Shield Brief W45 · 2 Nov – 8 Nov 2026
AI agents overstep, patient data in AI tools and a ChatGPT sandbox escape
AI security from the defender's side, every week: what changed, who is exposed and what stops it.
- Give every AI agent its own scoped identity, block cloud metadata and limit egress; autonomous agents will go as far as their access allows.
- Publish an approved AI tools list and data rules now; an academic medical centre had to notify patients after staff used AI tools without authorization.
- Update ChatGPT desktop clients and do not rely on one vendor safety mode to keep sensitive chats private.
Automotive suppliers
Your customer wants a TISAX® label. Know your gaps before the audit.
Answer the VDA ISA2027 control questions for your company and its locations. You get your maturity per chapter, scored like the ISA results sheet, and the findings an assessment would raise. ISA2027 applies to assessments ordered from 1 January 2027.
- Free readiness score and chapter results
- Likely major and minor findings
- €99 report with an AI action plan per gap
- Continue in the WardBee TISAX section, no scans needed
Self-assessment. It does not award a TISAX label.
Three ways we help
Platform
WardBee
Compliance automation for ISO 27001, SOC 2, NIST, CIS, and the EU CRA. Evidence collected from your cloud accounts and code repositories. From €39.
Explore WardBeeServices
Security engineering
DevSecOps engineering, threat analysis, and security advisory from engineers who work in the cloud every day.
See servicesOpen source
SentryHive, CostHive & Taglore
Free, open-source tools: SentryHive bundles security scanners, CostHive bundles FinOps reports, Taglore writes release notes from git tags.
Browse the tools
Built by Mr.D Apps
The engineers behind ScanComb
WardBee, SentryHive, CostHive and Taglore are built by Mr.D Apps: engineers who work in the cloud every day.
See what your evidence actually proves.
Connect a cloud account or repository with read-only access, and WardBee shows which controls are verified, which fail, and which are still unknown. Need a second pair of eyes? A ScanComb engineer can review the results with you.